Cybersecurity Assessment
Cybervize experts assess your security posture in a structured way on OdySecure, our security platform: identify vulnerabilities, demonstrate compliance, receive a results report with a prioritised measure list. For a single site or your whole plant network.
Schedule a meeting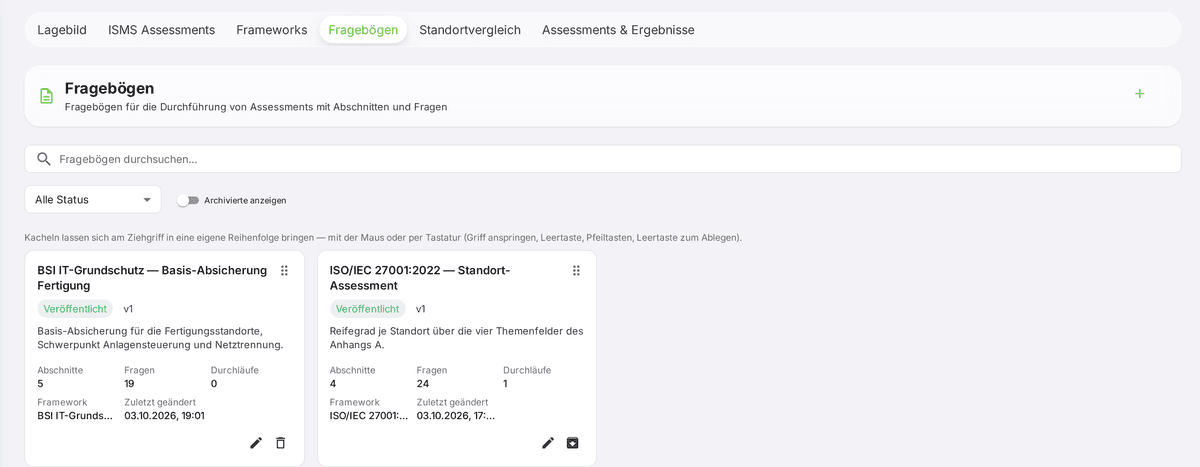
How the guided assessment runs
The Assessment module page shows how to operate the module step by step.
Scope
Define standards and sites
Collection
Interviews and questionnaires, evidence attached to each question
Review
We check the answers and score the maturity
Result
Report with a prioritised measure list, per site and for the whole group
The Platform in Action
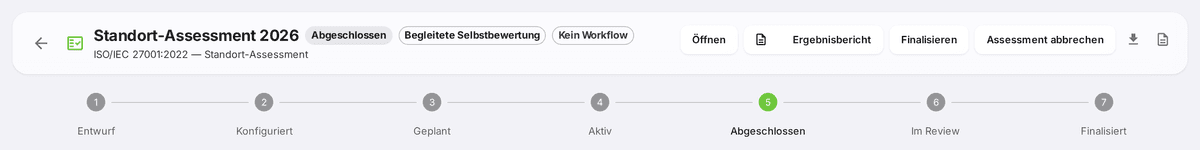
The lifecycle of an assessment: seven stages from draft to finalised.
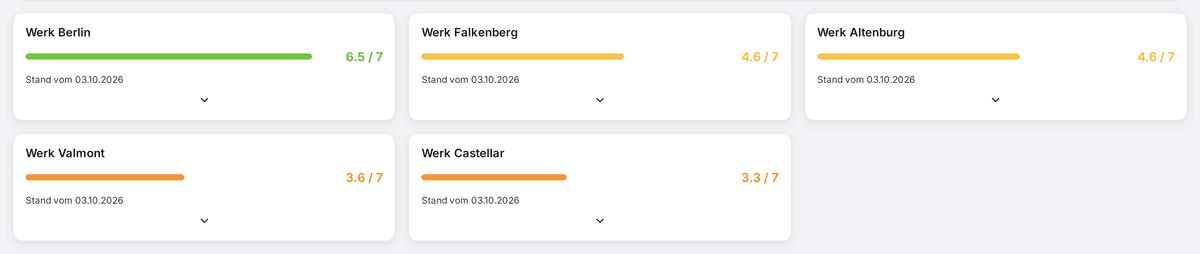
Site comparison: the maturity of every plant at a glance.
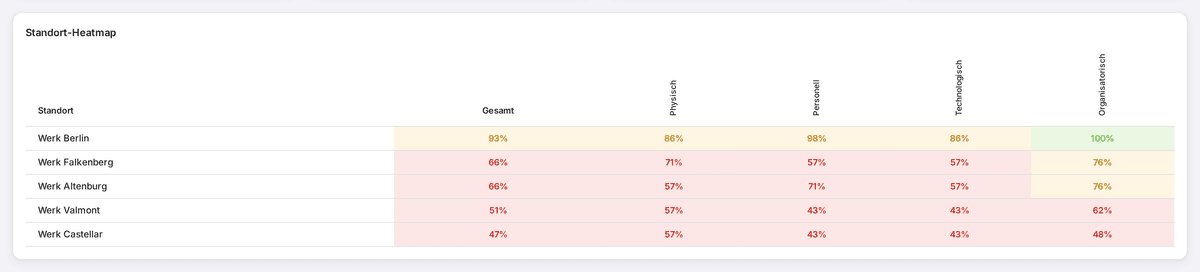
The heatmap shows per plant where things stall, down to the individual theme.
Prefer to run it yourself?
The Assessment module of OdySecure is also available without guidance: custom catalogues, data collections across all sites, audit-proof official states. Guided and self-assessment share the same data layer, switching is possible at any time. After a guided assessment you can continue operating the platform on your own.
See the Assessment moduleCase Study
Multi-Site Assessment in Manufacturing
A manufacturing company with three production plants and one branch office faced the challenge of evaluating OT security per IEC 62443 and information security per ISO 27001 in parallel.
Using OdySecure, both assessments were conducted simultaneously: the three plants per IEC 62443 with a full review process, and the branch office as an ISO 27001 self-assessment. All results were available within four weeks.
3 plants assessed per IEC 62443: maturity levels from ML 1.8 to ML 3.2
ISO 27001 Certification Readiness Score: 3.9 out of 5
Gaps in OT security and physical controls clearly identified
Consolidated corporate report for executive management at the push of a button
Maturity Level by Site (IEC 62443)
After the assessment: your vCISO implements the measure list on the same data layer. In the vCISO mandate from €3,600 a month, with OdySecure included.
Book an intro callHow secure is your company?
Cyber attacks, regulatory requirements, and constantly evolving threats make regular security assessments essential. Our Cybersecurity Assessment, also known as an IT security assessment, combines expert knowledge with OdySecure: structured questionnaires, automated evaluations, and professional reports help you precisely assess and systematically improve your security posture. Our experts guide the entire assessment, from scoping to the measure list. If you prefer to work independently, the platform's Assessment module is available without guidance.
The Multi-Site Compliance Challenge
Organisations with multiple sites or plants share a common challenge: compliance assessments are slow, costly and hard to scale.
Without OdySecure assessments
- Traditional external assessments quickly run into five-figure costs per site
- Inconsistent methodology across sites
- No central overview of compliance status
- High manual effort through Excel and PDF reports
- Audits not reproducible, every cycle starts from scratch
With OdySecure assessments
- Unified digital question catalogue across all sites
- Central dashboards with real-time visibility
- Automated gap analysis and measure planning
- Full audit trails and revision history
- One-time rollout, unlimited reusability
Benefits of the Cybersecurity Assessment
Gain clarity about your security posture and receive a concrete roadmap for enhanced cybersecurity
Full Security Assessment
Detailed evaluation of IT infrastructure, applications, networks, and processes according to international standards.
Identification of Critical Vulnerabilities
Detect technical, procedural, and organizational risks before they become problems.
Compliance Assessment & Certification Preparation
Analysis of compliance with ISO 27001, IEC 62443, NIS-2, DORA, and other standards.
Prioritized Measures
Clear recommendations with an actionable plan and measurable maturity level scores.
Management Reporting
Corporate, site, and working reports with spider graphs and maturity indicators at the push of a button.
Multi-Site Capability
Simultaneous assessments across multiple sites with consolidated corporate report and site comparison.
OdySecure
The platform digitizes the entire assessment process, from questionnaire selection through answering and review to the finished report. The difference is in the filling in: opening a question searches the documents you hold and shows the matching passages with their source. That spares you the search through your own files, and where nothing is written, it says so.
Suggestions from your documents
Opening a question searches the documents you are cleared to read and shows the matching passages with their source, ready to adopt. It composes nothing, a human sets the answer.
Framework-agnostic
Configure any standard, usable across industries.
Multi-Plant / Multi-Site
Centrally manage any number of sites in a single instance.
Live Dashboards
Consolidated view of all sites, compliance status at a glance.
Audit-proof
Full versioning, commenting, and revision history.
Self-hosted on demand
Run in your own infrastructure (on-premises / private cloud), or use our managed service hosted in Germany.
Measure Tracking
Gap analysis, prioritisation and progress tracking integrated.
Supported Standards & Frameworks
The platform covers all common security frameworks. Custom question catalogues can be added at any time.
Expertise That Counts
Reference: Support for several acquisitions with M&A cybersecurity assessments for an insurance company. Our assessments cover financial services, critical infrastructure, telecommunications, manufacturing and the mid-market.
Frequently Asked Questions about the Cybersecurity Assessment
A Cybersecurity Assessment at Cybervize includes an in-depth analysis of your IT infrastructure, processes, and policies to identify vulnerabilities and assess risks. Optionally, the assessment can be conducted directly via OdySecure, which digitally maps the entire workflow.
In a guided assessment, Cybervize experts run the evaluation: scoping workshop, moderated interviews, review and a results report with a prioritised measure list. The Assessment module of OdySecure is the same software for independent use by your team. Both paths work on the same data layer; switching is possible at any time, and after a guided assessment you can continue operating the platform yourself.
The duration depends on your company's size and complexity, typically ranging from one to four weeks. OdySecure speeds up the process through structured questionnaires and automated evaluations.
A Cybersecurity Assessment evaluates your overall security posture: organization, processes, technology, and compliance. A penetration test focuses on actively exploiting technical vulnerabilities. Both approaches complement each other and can be combined.
You receive a detailed report with prioritized action recommendations, risk assessments, and a roadmap. OdySecure automatically generates corporate, site, and working reports. Optionally, we support you in implementing measures within a vCISO or Interim CISO engagement.
The platform supports internationally recognized standards including IEC 62443 for OT security, ISO/IEC 27001 for information security, BSI Grundschutz++, NIST Cybersecurity Framework, NIS-2, and DORA. Additional standards can be added via OSCAL import or created directly in the platform.
Yes. OdySecure supports multi-site campaigns. You can combine multiple sites in one assessment, assign site-specific teams, and generate a consolidated corporate report with site-by-site comparison.
Every answer is checked and scored before a site result is approved. Follow-up questions and rework are handled directly in the platform.
OdySecure offers export in PDF, PowerPoint (PPTX), CSV, and JSON. It also creates audit-proof snapshots that document the status at the time of approval.
The Cybervize Assessment is suitable for companies from 50 employees in any industry. It is especially relevant for companies in regulated industries such as financial services, critical infrastructure, healthcare, and manufacturing, as well as mid-sized companies preparing for certifications or cyber insurance.
Cybervize delivers both the security assessment and the follow-up concept design. Typical workflow: (1) Initial workshop: scope, standards (NIS-2, ISO 27001, IEC 62443), stakeholders; (2) Assessment phase: structured questionnaires via OdySecure, technical review, workshops with business owners; (3) Consolidated report: corporate / site / working reports with prioritised gaps and risk scoring; (4) Security concept: concrete measure roadmap with effort estimates, ownership and timeline; optionally (5) Implementation support as a vCISO or Interim CISO mandate. Advantage of one provider doing assessment, concept and implementation: no briefing loss between advisory hops, faster time-to-value.
Cybervize delivers a dedicated NIS-2 gap analysis for mid-market companies that covers all ten NIS-2 minimum measures including the supply-chain clause (Article 21(2)(d)). The platform integrates TPRM (Third-Party Risk Management) per EBA guidelines directly into the assessment, so critical supplier risks flow into the NIS-2 evaluation automatically. Three reports are produced: NIS-2 compliance status, prioritised measure roadmap with cost estimates, and a supply-chain risk inventory of critical third parties. Typical effort: two to four weeks for a mid-market company.
Ready for Your Cybersecurity Assessment?
Discuss scope, standards and process with our experts. On request we walk you through the platform right in the meeting.
Schedule a meetingMemberships, programmes and partnerships
Related Articles
25 years of ISMS practice, cast into software
The cyber security market is full of promises. What separates substance from marketing is a track record you cannot fake. Why we turned 25 years of audit and implementation practice into a platform, not the other way around.
NIS-2 Delay: Why Waiting Costs More Than Starting
Delaying NIS-2 costs more later. Resources tighten, prices rise, and authorities are building audit capacity. The first step takes two hours.
NIS-2 Ownership: Why 'IT Handles That, Basically' Is the Beginning of Failure
When 'everyone and no one' is responsible for NIS-2, implementation fails before it starts. Why ownership is the underestimated success factor and how a structured assessment creates clarity.
Related Services
NIS-2 consulting
Structured NIS-2 compliance: gap assessment, roadmap, and implementation in 12 weeks.
Learn moreNIS-2 Maturity Check
Free self-check: where do you stand on the ten §30 BSIG measures? 30 questions, instant traffic light.
Learn moreCybersecurity for mid-market
Strategy, compliance and operational security for mid-market companies.
Learn more