AI for your information security. And security for your AI.
Meet NIS-2, DORA, ISO 27001. With a CISO you don't have to hire.
Cybervize takes on the CISO function in two ways. As a Virtual CISO permanently, with a fixed capacity of two to six days per month, from 3,600 euros per month. As an Interim CISO for a fixed term, when the role is vacant or an incident has to be worked through; that route is priced per engagement. Alongside it the ISMS platform OdySecure for IT and OT, from mid-market to enterprise: ISMS, BCM, Assessment and Third-Party Risk Management with security assessments against ISO 27001, IEC 62443, BSI Grundschutz++, NIST or your own standards. AI under your own control, data residency in Germany.
We take on the CISO function. Interim until the role is filled, or permanently. As a vCISO from €3,600 per month.
Intro call: free, 30 minutes, with a senior CISO.
References
- Moonfare: Cybervize as Interim CISO for the DORA implementation and the ISO 27001 audit
- Support with the introduction of NIS-2 in the energy sector
- Carve-out as Interim CISO: building up information security at an international mechanical engineering company
- Support for several acquisitions with M&A cybersecurity assessments for an insurance company
Monthly report
Example
Information security
To the management board
Overall status: On track. One decision is open.
1 Status of requirements
| Status light | Requirement | Status | Implementation in per cent |
|---|---|---|---|
| amber | NIS-2 | in progress | 72 % |
| green | ISO 27001 | audit-ready | 91 % |
| amber | Supplier questionnaires | 11 of 14 | 79 % |
2 Situation
- Risks above tolerance
- 3
- Next audit
- in 6 weeks
3 For decision
Residual risk, legacy accounting system
- accept until Q1
- bring replacement forward
Your vCISO
Evidence in OdySecure
Page 1
Memberships, programmes and partnerships
The CISO function, filled.
A senior CISO takes on the role in your organisation and leads your NIS-2, DORA or ISO 27001 work until it can be evidenced.
A filled function
We carry out the work and keep your executive board informed (C-level reporting).
Evidence in OdySecure
The work runs on our platform. The licence is included in the mandate.
Support through audits
We prepare audits and inspections with you and support you on the day.
- Basicfrom €3,600 a month, approx. 2 days
- Standard€4,900 a month
- Seniorapprox. €8,500 a month, 5 to 6 days
Minimum term 6 months, then cancellable monthly.
What each tier includes- Regulatory requirementsNIS-2, DORA or ISO 27001 must be met and evidenced. vCISO
- VacancyYour CISO post is open. An interim CISO bridges the gap for a fixed term, project-based at €8,000 to €15,000 a month. Interim CISO
- Acquisition or carve-outAfter closing, build the security function in the acquired company or in the carved-out unit. M&A support
Client voices
“Alexander Busse supported us with Cybervize as Interim CISO in the DORA implementation and the ISO 27001 audit. We achieved both.”
 Lorenz Jüngling, Co-CEO & Managing Director, MoonfareTranslated from the German original.A reference call is available on request, arranged through us.
 Lorenz Jüngling, Co-CEO & Managing Director, Moonfare
“Alexander has really convinced me, both with his cybersecurity expertise and his personality. He provides very professional and effective support to the task of further improving our cybersecurity management. Any organization would be lucky to be supported by Alexander and his methodology.”
Your vCISO works with OdySecure.
Your vCISO runs your information security management system in OdySecure, our own platform. The requirements that apply to your organisation, for example from NIS-2, DORA or ISO 27001, sit there alongside risks, measures and evidence in a single data set. That is why evidence is produced in day-to-day operations rather than in the days before the audit, and why the monthly report to your management board comes from the same data. The platform is included in the mandate. Cybervize developed it from its own consulting practice, funded by the German federal government's StartupSecure programme and in a 14-month partnership with the CISPA incubator, the Helmholtz Center for Information Security.
Two routes, one firm
The vCISO mandate fills your CISO role and implements the regulatory requirements your organisation faces, with OdySecure as our tool. If the role is already filled on your side, license the platform on its own. Both run on the same data foundation, are operated in Germany and stay under your control.
Virtual CISO
We fill your CISO role part-time and remotely, on a long-term basis. The platform is included in the mandate and carries the evidence.
- Mid-market companies without full-time CISO budget
- Continuous NIS-2 or ISO 27001 compliance management
- Strategic partner instead of one-time project consultant
2 to 6 days/month | From €3,600/month, platform included
See the vCISOPlatform licence
Your CISO is on board and you need the tool. Module licence, with an onboarding project on request, then ongoing operation by your internal team.
- In-house CISO function already established
- Replace Excel and Word ISMS, build an audit trail
- Migration from an existing GRC suite
Module licence | Migration 6 to 10 weeks | Onboarding to self-service 6 to 12 months
See the platformVacancy or crisis? An Interim CISO takes over for 3 to 12 months, on-site if needed. Go to Interim CISO
All our services on one page: vCISO, NIS-2, ISO 27001 and more. Cybersecurity for mid-market companies
Only need to know whether NIS-2 applies?
In the risk check we establish in 30 minutes whether NIS-2 applies to your company and which five gaps matter most. Free and without obligation.
Book the risk check The journey in 5 stations
OdySecure is an Agentic ISMS, an ISMS platform in which the AI derives risks, measures, controls and policies from your documents and answers questions with sources. We call the model behind it the ISMS operating system: requirements, risks, measures and evidence come together in one connected data model. Compliance is created in operations, not next to them. What an Agentic ISMS is
OdySecure amplifies the effectiveness of your security lead or team. ISMS, risk management, assessments, BCM and third-party risk management in one system. With built-in LLMs, Made in Germany.
Discover the platform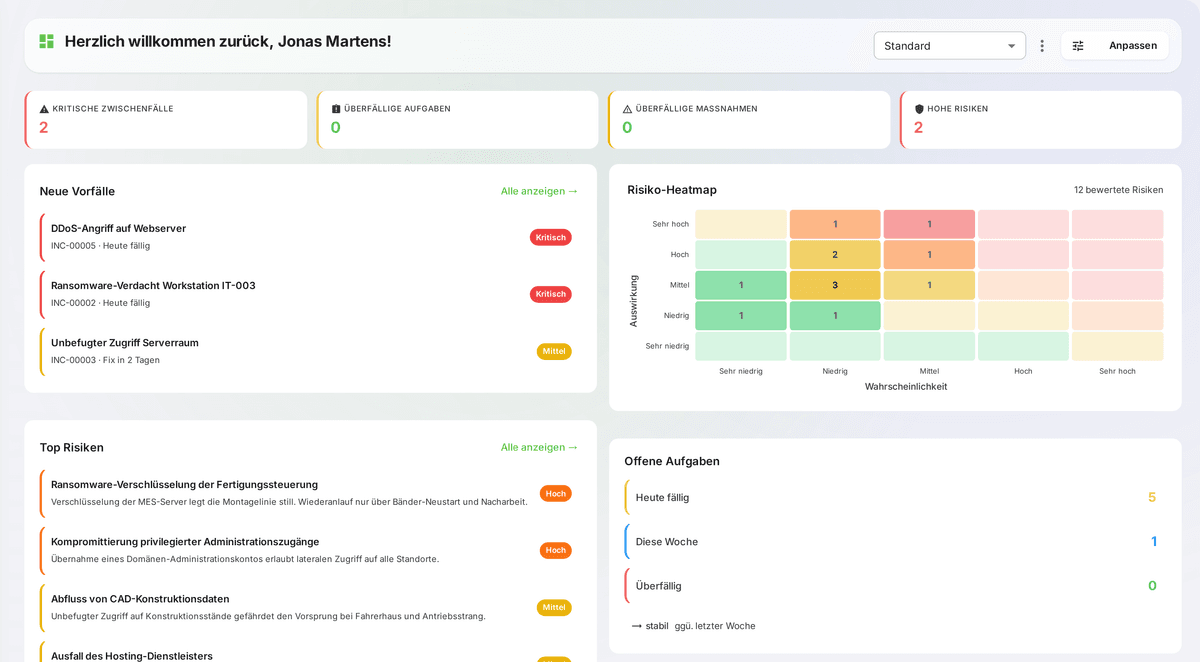
Everything in one place
No switching between tools. From assessment gaps you create measures with one click, BIA data validates BCM plans, supplier risks link to assets.
AI as a teammate
Integrated LLM service assists with risk assessment, contract analysis and assessment summaries. Hosting exclusively in Germany.
What the AI takes over
You do not fill in an ISMS. You feed it your documents.
OdySecure derives what applies in your organisation from your documents and your structure: from business process to security process, each station a proposal a human accepts. Under a vCISO mandate, your vCISO does this for you.
- 1Business process
- 2Asset
- 3Risk
- 4Measure
- 5Control
- 6Policy
- 7Security process
A human decides at every station. The AI proposes; you accept the proposals one by one or per station, and each approval records who signed it off.
Where do we stand?
Ask your ISMS. Every answer comes with its source. Your questions are logged for audit.
Management teams, supervisory boards and auditors all ask the same question. The AI layer of OdySecure answers it from your real data, not from assumptions.
OdySecure Navigator: sourced answers
AvailableThe assistant answers questions like "What are our biggest risks?" or "Are we audit-ready?" from your tenant's real data: around 25 vetted queries, every answer with source and metric, strictly within read permissions. If there is no data or no read permission, it says exactly that. On your instruction it also carries out actions in the system, such as linking a measure to a risk or creating a task. Nothing runs until you have confirmed its plan, and it always works within your own permissions.
AI agents: acting with approval
Design-partner programmeAI as an employee: its own account, roles, a visible AI-agent badge. Suggesting is the default; acting is limited to narrowly defined fields and requires four-eyes approval. Hard locks always apply: no closing incidents, no risk acceptance, no approvals, no granting of rights. First use case: initial incident triage with indicative NIS-2 deadline hints.
Sovereign in operation, humans stay accountable
This is how the AI layer is built (OdySecure Navigator available, AI agents in a design-partner programme, not yet generally available):
- Sovereign mode: local LLM operated in Germany, no data passed to external model providers.
- AI system inventory: every agent is added automatically; a human classifies and confirms before activation. This is your own record, not a filing with any authority.
- Human in the loop: a kill switch pauses any agent instantly, access keys expire at the term set for them, actions are in the audit log.
Ask first, then act, always verifiable.
Sovereign AI
One AI for your whole company, and it stays inside your network
Your staff draft texts and work through documents, and the AI also reads scans with handwriting. The model runs on hardware in your building, no request goes to a model vendor, and OdyControl documents its use.
Talk to us about your CISO function.
In the intro call we establish which requirements apply to your organisation and how we would fill the CISO role. Free, 30 minutes, with a Senior CISO.
Book an intro callThe Cybervize Podcast
Cybersecurity insights: Interviews with CISOs from Vodafone, Red Bull, Trade Republic and more.
Cybervize Podcast on Spotify
Spotify sets cookies. By clicking you consent to data transfer to Spotify.
Latest from our Blog
Practical insights on cybersecurity, NIS2, AI governance and CISO strategies.
What is an Agentic ISMS, and what stays with people?
In an Agentic ISMS, AI agents derive risks, measures and policies from an organisation's own documents and carry out tasks in the system. A person sets how far an agent may act on its own. OdySecure enforces these limits outside the language model.
AI attacks this week: State-aligned group uses AI agents to attack through ConnectWise (week 43/2026)
According to Microsoft, a China-state aligned group automated its attack on ConnectWise with the AI tool ARTEX and then went after more than 2,250 Microsoft 365 tenants. Also this week: breaches at platforms that were about keys for AI services, and AI agents that broke into the websites of more than 100 companies.
The 2026 flood of vulnerabilities: what AI has changed
AI finds vulnerabilities faster than teams can close them. In August 2026, more than twice as many were published as in January. Management should therefore set which flaws come first and who decides about the rest.
Working with Cybervize: three routes
IT service providers and MSSPs serve their clients in separate tenants in OdySecure, with their logo in the reports. Consulting firms run assessments and advisory engagements on the platform. Freelance vCISOs lead mandates that Cybervize wins, with OdySecure as their tool.
Become a partner