Financial services
Banks, insurers, payment service providers, BaFin-regulated entities. We know DORA from practice: as Interim CISO for a financial services firm during DORA implementation and its ISO 27001 audit.
- DORA
- MaRisk
- Bundesbank audit
Regulated industries with their own NIS-2, DORA or KRITIS exposure. Per sector: the relevant obligations and the matching Cybervize building block.

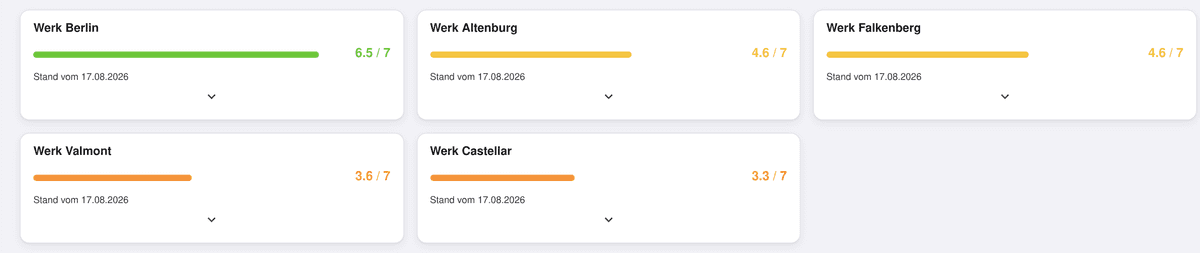
Each sector has its own obligation profile (NIS-2 annex, DORA, TISAX, BSI, MDR, § 391 SGB V). Our vCISO leads the implementation of the information security obligations that follow from it and works with OdySecure, the security platform by Cybervize.
Banks, insurers, payment service providers, BaFin-regulated entities. We know DORA from practice: as Interim CISO for a financial services firm during DORA implementation and its ISO 27001 audit.
OEMs, Tier-1 and Tier-2 suppliers with TISAX requirements (contractual, not statutory), OT/IT convergence in production and supply-chain risk management under NIS-2 and ISO 27001. UN R155/R156 for type-approval relevant vehicle topics.
Defense companies and security-critical suppliers. VS-NfD experience, ISO 27001, ITAR/EAR-aware supply-chain work.
No dedicated sector page. Entry via the assessment.
Electricity, gas, heat and hydrogen utilities in KRITIS scope. NIS-2 Annex I, IT-Sicherheitskatalog (electricity/gas) and BSI IT-Grundschutz. Per-site OT maturity becomes comparable through the platform.
Federal agencies, state authorities, municipal bodies and public enterprises. Experience with highly confidential projects, ISO and NIST and BSI IT-Grundschutz.
No dedicated sector page. Entry via the assessment.
Classic mid-market sectors with OT/IT convergence in production, supply-chain pressure from enterprise audits and rising threat exposure. NIS-2 Annex II plus Cyber Resilience Act for connected products.
Managed service providers and managed security service providers are listed in Anlage 1 BSIG where the entity definition and size thresholds are met; other IT firms usually face supply-chain requirements from their clients. Multi-tenant platform use is supported.
NIS-2 Annex II (Anlage 2 BSIG, manufacture and trade of chemical substances). We cover OT security in plants and supply chains and the interface with process safety; the obligations under the Major Accident Ordinance (SEVESO) themselves stay with the operator.
Hospitals, MVZ groups, medical device manufacturers and health-IT providers. NIS-2 Annex I by entity type and size, § 391 SGB V for hospitals, and the cybersecurity requirements of the MDR.
NIS-2 Annex II covers industrial production, processing and wholesale. IFS Food and FSSC 22000 are private food safety standards, not laws; we take on the information security side, across several plants where needed.